
Corporate sign-in
Use your company account to sign in to BusinessProxy.
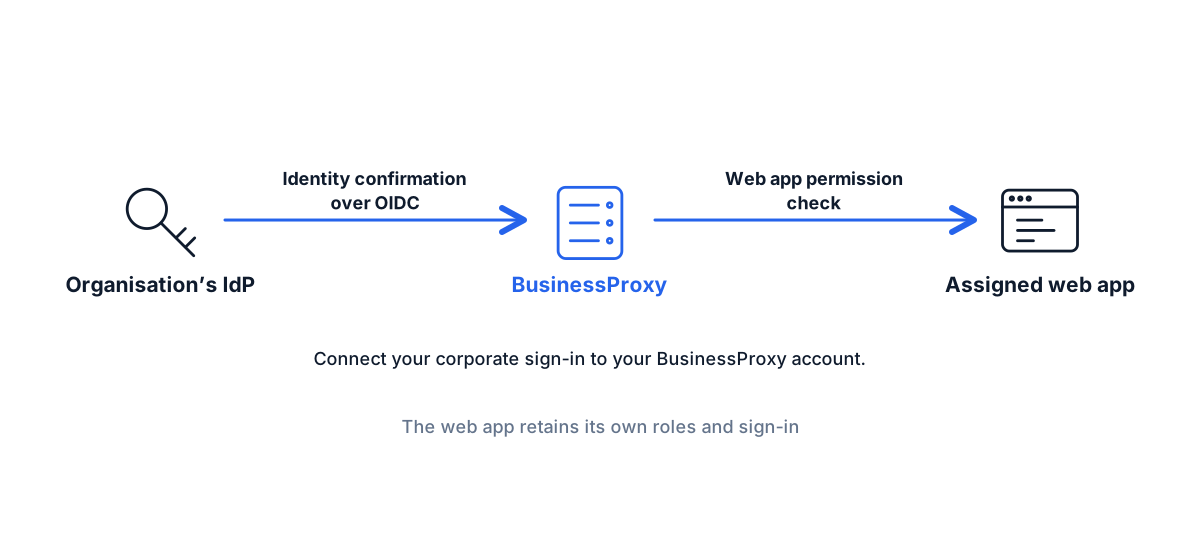
Connect your company’s sign-in provider using OpenID Connect (OIDC). Users link their accounts and can then sign in through the company provider. Administrators grant web application access separately.
The user explicitly confirms the account link
An administrator connects the provider
They configure the issuer, client ID, secret and callback URL using the OIDC guide.
The user links their accounts
They open account settings in BusinessProxy, verify their identity again and sign in with the company provider.
Future sign-ins use the organisation’s provider
The user chooses corporate sign-in. BusinessProxy then checks which web applications they are allowed to access.
Verified connections and other providers
| Option | What to consider |
|---|---|
| AD FS over OIDC | Account linking and subsequent sign-in have been verified with AD FS. |
| Another OIDC provider | Validate discovery, issuer, callback, token signatures and claims with your configuration. |
| User creation and linking | The administrator chooses how accounts are created and linked. Connecting OIDC does not itself import the full employee directory. |
Who controls sign-in and permissions
The company provider verifies the employee’s identity. A BusinessProxy administrator decides which web applications they may open. Permissions inside a CRM or CMS are still managed in that web application.
When an employee changes roles or leaves the company, update their access in BusinessProxy and in the web applications. Connecting corporate sign-in does not replace those steps.
- Explicit linking and unlinking
- Identity verification before changing a link
- Separate web application permissions
- A tested backup sign-in method